Across the Industry Brief – Issue 32
Microsoft is taking a bold step in the education sector by offering US school districts enforceable AI privacy protections in contracts, addressing growing concerns over student data usage. Meanwhile, Colorado is advancing its AI regulations with formal rulemaking on automated decision-making and chatbots, setting a precedent for other states. In the financial realm, banks are blocking AI agents from accessing accounts as the stalled US open banking rule leaves access governed by private policies. These developments highlight the evolving landscape of AI governance and the urgent need for organizations to adapt to new compliance expectations. Read more to stay informed!
One Program, Not Four: Why ARISE Framework® v2.1 Is a Governance Operating System
Most organizations face a coordination problem rather than a governance capability issue. With multiple programs running in silos—security, privacy, legal, and now AI—gaps in oversight create risks. The newly released ARISE Framework® v2.1 acts as a governance operating system, unifying these functions under one comprehensive structure. By organizing 128 controls across seven domains, ARISE simplifies compliance with evolving regulations like the EU AI Act and GDPR. This innovative approach allows organizations to absorb new statutes seamlessly, transforming governance from a fragmented effort into a cohesive strategy. Discover how ARISE can streamline your governance and enhance your risk management.
Minimum Evidence for an AI System
The ten artifacts every deployed AI system must be able to produce on demand; what each contains, who will ask for it, and how to generate the package continuously as a side effect of operation rather than assemble it under pressure.
What Is a Chief Responsible AI Officer (CRAIO)?
A Chief Responsible AI Officer (CRAIO) is the executive accountable for AI governance, risk, and assurance. What the role does, how it differs from a CAIO and CISO, and when a virtual CRAIO fits.
Assessed Signal – October 2026
California enacted landmark workforce AI regulations barring automated terminations without human review and creating an auditor certification framework, while federal lawmakers proposed a Commerce Department AI Safety Board. Concurrently, a surge of cyberattacks impacted major Japanese organizations, highlighted by ransomware disruptions at Keio Corporation and account breaches at Nikkei. Meanwhile, security researchers documented autonomous AI agents executing rapid zero-day exploits and credential theft across enterprise environments. As Microsoft noted vulnerability weaponization speeds dropping under 24 hours, studies show organizations adopting AI agents faster than their governance controls. Operational resilience now requires active containment and accounting for surrounding autonomous systems.
Across the Industry Brief – Issue 31
In the latest issue of Across the Industry Brief, significant developments unfold in AI policy and regulation. The Department of Homeland Security has barred federal agencies from using DeepSeek, a Chinese AI product, citing national security risks. Meanwhile, Anthropic faces backlash over its draft AEGIS safety bill, highlighting the challenges of shaping federal AI legislation. Additionally, NIST and CISA are collaborating on guidance for AI agent training incidents, marking a crucial step in federal cybersecurity. As organizations navigate these changes, understanding the implications for compliance and vendor risk becomes essential. Dive into the full report for more insights!
ARISE Framework®: The Governance Operating System
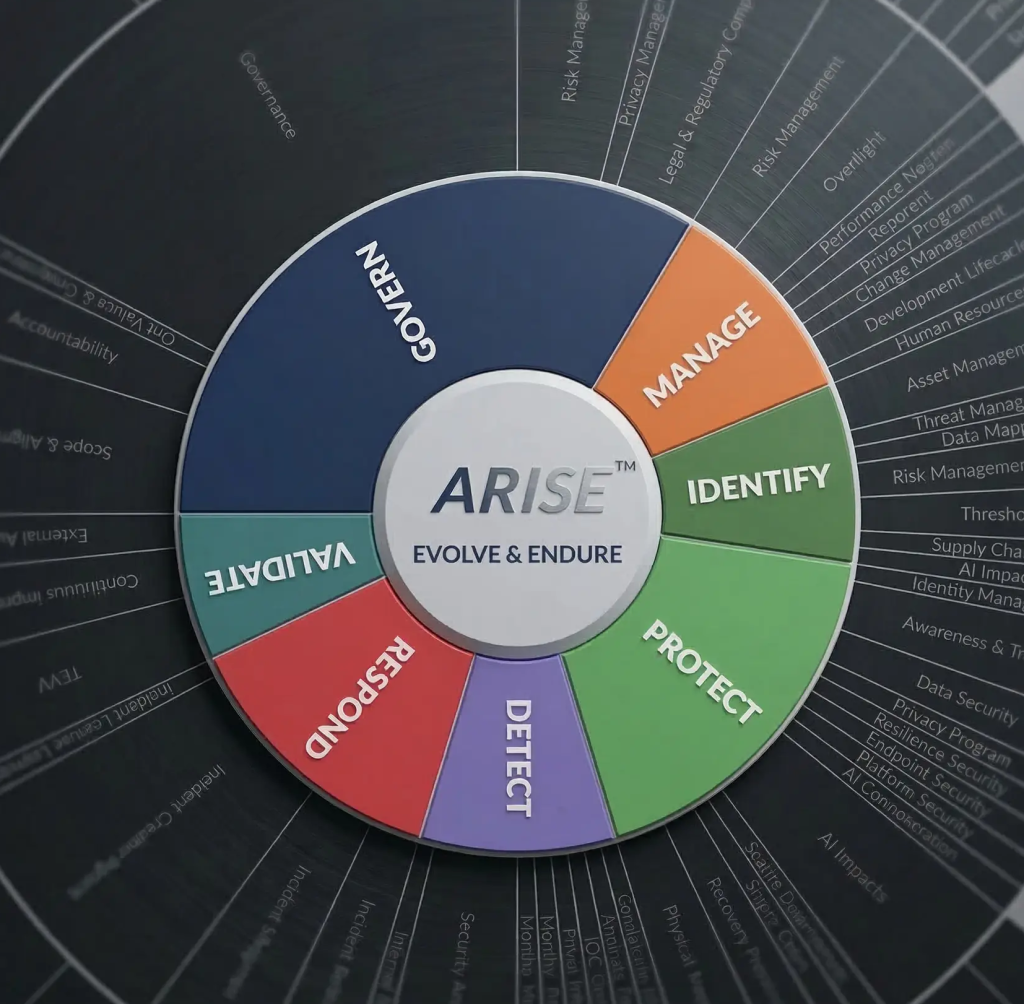
ARISE Framework® is the Governance Operating System for AI, cybersecurity, privacy and ethics: 128 controls, 953 requirements, seven domains and 40 published crosswalks, giving leadership one common operating picture.
The Governance Operating System: Why ARISE™ Replaces Four Programs With One Picture
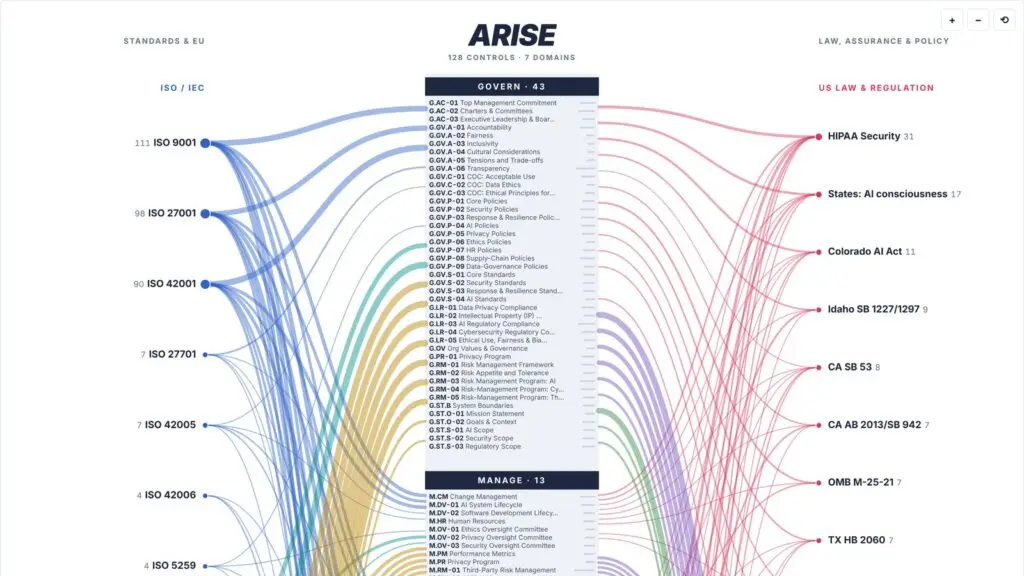
Most organizations have a coordination problem, not a capability problem. A Governance Operating System is one control framework implemented once and mapped to every law and standard. ARISE Framework® is built as one, and the crosswalk map shows why.
Across the Industry Brief – Issue 30
Regulators on both sides of the Atlantic are ramping up enforcement against leading AI labs, with the FTC issuing civil investigative demands to OpenAI and Anthropic, while the EU opens its first AI Act probes. This unprecedented convergence of federal, international, and state actions highlights the urgent need for organizations to bolster their AI security and compliance measures. As California mandates independent verification and kill switches for AI, and Anthropic proposes a controversial federal safety bill, the landscape of AI governance is rapidly evolving. Discover how these developments could impact your organization and the future of AI regulation.
Supporting the Oregon AI Accelerator for a Second Year
Assessed Intelligence returns as a supporter of the Oregon AI Accelerator as 14 AI-native startups begin Cohort 2, continuing our work with founders building secure and responsible technology.