ARISE Framework® · Assurance of Responsible, Innovative, and Secure Environments
The Governance Operating System
ARISE Framework® is the Governance Operating System: one control structure that an organization runs its AI, cybersecurity, privacy and ethics governance on. Implement it once. Map every law and standard to it. Give the board a common operating picture.
40 Published Crosswalks to Laws, Standards & Assurance Criteria
NIST AI RMF
NIST SP 800-53
ISO/IEC 42001
ISO/IEC 27001
ISO/IEC 27701
ISO 9001
EU AI Act
prEN 18228–18286
GDPR
HIPAA Security Rule
PCI DSS v4.0
BSI C5
Colorado AI Act
Texas TRAIGA
OECD AI Due Diligence
THE COORDINATION PROBLEM
You Cannot Govern Four Programs With Four Pictures.
Most organizations do not have a governance capability problem. They have a coordination problem. Security, privacy, legal and data science each run their own program against their own framework, and the risk sits in the gaps between them.
A SOC 2 trail, an ISO 42001 document set, a privacy program and an AI committee each tell leadership something different, and none of them tell it the whole thing. ARISE Framework® is the Governance Operating System under all four. It replaces four partial views with one common operating picture, and it makes VALIDATE part of the system rather than an afterthought.
“There can be no responsible technology without secure technology.”
— Foundational Principle of ARISE™
Where the gaps sit
AI, cybersecurity, privacy and ethics run as four parallel programs with four vocabularies
Each new law or standard becomes a new project instead of a delta against existing controls
The same evidence is collected three times for three different assessors
No single status view that the board, the CISO, the privacy officer and legal read the same way
Validation treated as an afterthought rather than part of the system
WHAT IS ARISE™
One System. Four Programs. One Common Operating Picture.
The ARISE Framework® is a Governance Operating System: one control structure that an organization runs its AI, cybersecurity, privacy and ethics governance on. Published by Assessed Intelligence, it provides 128 controls and 953 requirements across seven domains and maps outward to 40 published laws and standards, including the EU AI Act, ISO/IEC 42001, ISO/IEC 27001, NIST AI RMF and NIST SP 800-53.
ARISE™ closes the gaps structurally. A control that serves two domains is written once and governed once. Each new law becomes a delta against the existing control set rather than a new project. The result is a common operating picture: one evidence base and one status view that the board, the CISO, the privacy officer, legal and data science all read the same way.
Prioritized requirements, each with a permanent, citable ID
Domains
0
One control written once serves AI, cyber, privacy and ethics
Published Crosswalks
0
ISO, NIST, EU AI Act, HIPAA, PCI DSS, state AI laws and more
EU Harmonised Standards
0
prEN 18xxx drafts for the EU AI Act, each crosswalked to all 128 controls
Implementation Tiers
0
Foundational (337), Operational (452), and Advanced (164) requirements
FRAMEWORK ARCHITECTURE
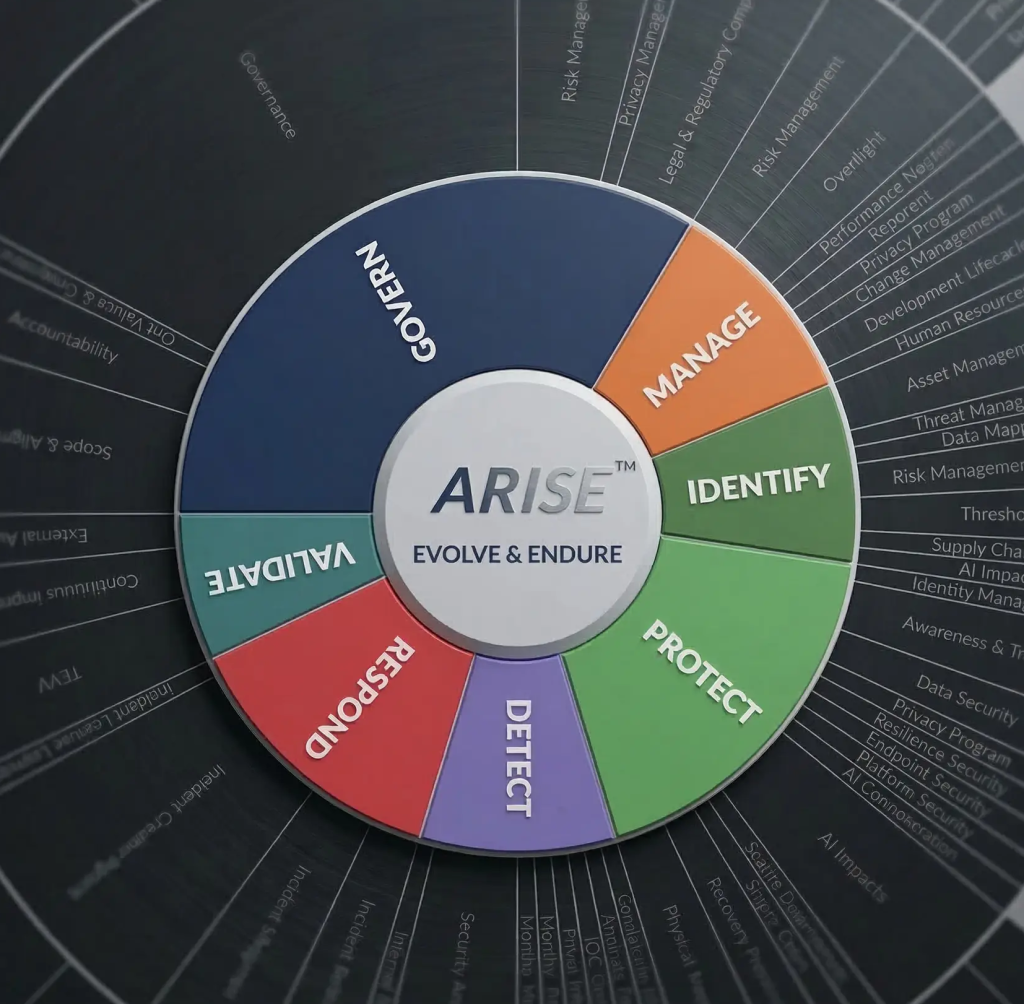
The Seven Domains of ARISE™
Each domain governs a defined scope toward a defined outcome. A control written in one domain serves AI, cybersecurity, privacy and ethics at once, so the seven together form a single assurance cycle rather than four parallel ones.
Accountability, policy, risk appetite, the privacy program, legal and regulatory obligations, third-party governance.
Manage
Lifecycle and change control, AI risk, workforce, oversight committees, third-party risk, privacy operations.
Identify
Asset and AI system inventory, data mapping, supply chain, risk classification and thresholds.
Protect
Identity and access, data, model, network and endpoint security, cryptography, resilience.
Detect
Continuous monitoring, anomaly and drift detection, assessments, third-party monitoring.
Respond
Incident response for cyber, AI and privacy events, communications, lessons learned.
Validate
Testing, evaluation, internal and external audit, independent assurance, continuous improvement.
IMPLEMENTATION GUIDANCE
Tiered Implementation Across the Control Set
Every one of the 953 requirements carries a priority tier, which gives an organization a defensible sequence for implementing the operating system. Start with the foundation, then build depth.
0
P1
Foundational
0
P2
Operational
0
P3
Advanced
Foundational | P1 (337 requirements)
The ground-floor requirements every organization must establish first — the structures, policies, inventories, and safeguards that must be in place before operational or advanced controls can be meaningful.
Operational | P2 (452 requirements)
The active, ongoing requirements that keep governance working across live environments — driving continuous monitoring, risk management workflows, oversight cadences, and vendor management activities day to day.
Advanced | P3 (164 requirements)
The high-maturity requirements that distinguish programs capable of demonstrating assurance under independent scrutiny — deeper testing, cross-domain correlation, and the evidentiary posture needed by regulators and auditors.
Each of the 953 requirements is assigned a priority tier so every organization, regardless of starting maturity, has a clear and defensible path to continuous assurance.
Implement Once. Absorb Every Statute as a Delta.
Standards and statutes map to ARISE™, not the other way around. The six CEN/CENELEC prEN 18xxx harmonised standards for the EU AI Act each cover all 128 controls, so an organization running on ARISE™ maps its existing evidence as they land instead of building a separate conformity program.
IN PRACTICE
What unified governance looks like in practice
The strongest organizations do not wait until regulation or an incident forces governance onto the roadmap. They build it into operations as technology adoption grows.
An organization needed to move beyond fragmented oversight and establish a repeatable governance model for AI, cybersecurity, and emerging technology across critical business functions.
Clear roles and accountability across the technology lifecycle
Visibility into AI systems, dependencies, and operational risk
Continuous monitoring and control assurance
Evidence for regulators, auditors, and leadership
A unified governance model that scales with adoption
How We Help
Assessed Intelligence implements, operates and validates ARISE Framework®, the Governance Operating System, for organizations that want help. Adoption does not require an engagement: the framework, its requirements and all 40 crosswalks are maintained in a public repository under the ARISE™ Public Use License (Non-Commercial).
ARISE™ is built for organizations that answer to more than one regulator or assessor at once: healthcare systems under HIPAA and state AI laws, defense contractors under CMMC, financial firms with model risk obligations, and any organization deploying AI agents under the EU AI Act, the Colorado AI Act or Texas TRAIGA.
What organizations will achieve
Organizations working with Assessed Intelligence will demonstrate governance to regulators and auditors, expand technology use cases with oversight in place, and give boards the evidence they need to maintain confidence.
Satisfy regulators and auditors with structured, documented evidence of governance
Scale AI and technology adoption with controls that keep pace with operational complexity
Give leadership one common operating picture of risk, controls, and assurance posture
Build accountability across AI, cybersecurity, and ethics before it becomes a gap
Produce audit-ready evidence without burdening technology or operations teams
Move faster with the confidence that comes from knowing foundations are sound
HOW WE HELP
Implement. Operate. Validate.
Assessed Intelligence delivers the Governance Operating System through three service pathways, each designed for a different stage of your governance program.
Implement
Build the governance foundation
We help organizations establish the structures, policies, controls, and lifecycle processes needed to govern AI and emerging technology responsibly.
Every OPERATE engagement runs on ARISE Framework®, the Governance Operating System. Your fractional vCISO or vCRAIO inherits a working control set and a common operating picture on day one rather than building both from scratch.
Most governance programs fail on coordination, not capability. ARISE™ fixes the coordination structurally.
One system, four programs
AI, cybersecurity, privacy and ethics run on the same controls, the same owners and the same evidence, instead of four parallel programs with four vocabularies.
Implement once, map outward
Standards and statutes map to ARISE™, not the other way around. Each new law becomes a delta against the existing control set rather than a new project.
One evidence base, many assessors
A single control and its evidence can satisfy an EU AI Act conformity reviewer, a HIPAA risk analysis and a CMMC assessor.
One control, governed once
Incident response for AI, cyber and privacy is R.IR-01, R.IR-02 and R.IR-03 in one RESPOND domain, owned by one function, not three playbooks in three teams.
Validation built in
The VALIDATE domain makes testing and independent assurance part of the system rather than an afterthought.
A common operating picture
Leadership works from one view of governance status, so a finding in one domain is visible to every other domain at once.
OPEN FOR ADOPTION
Build Governance That Holds Up Under Scrutiny
ARISE Framework® is the Governance Operating System for AI, cybersecurity, privacy and ethics: 128 controls, 953 requirements, seven domains and 40 published crosswalks. It is open for adoption under the ARISE™ Public Use License (Non-Commercial). Internal governance, education, research, compliance readiness and nonprofit use are free; selling ARISE™-based services, paid audits against it or paid products built on it require a commercial license.
To provide the best experiences, we use technologies like cookies to store and/or access device information. Consenting to these technologies will allow us to process data such as browsing behavior or unique IDs on this site. Not consenting or withdrawing consent, may adversely affect certain features and functions.
Functional
Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes.The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.
To provide the best experiences, we use technologies like cookies to store and/or access device information. Consenting to these technologies will allow us to process data such as browsing behavior or unique IDs on this site. Not consenting or withdrawing consent, may adversely affect certain features and functions.
Functional
Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes.The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.